Stop Asserting Compliance. Prove It Inside Your Tenant.
Screenshots, spreadsheets, and static attestations are not evidence. PolicyCortex runs directly inside your own cloud tenant—sealing every observed control state, every approved change, and every policy-gated automated action into an append-only record that an assessor can independently verify.
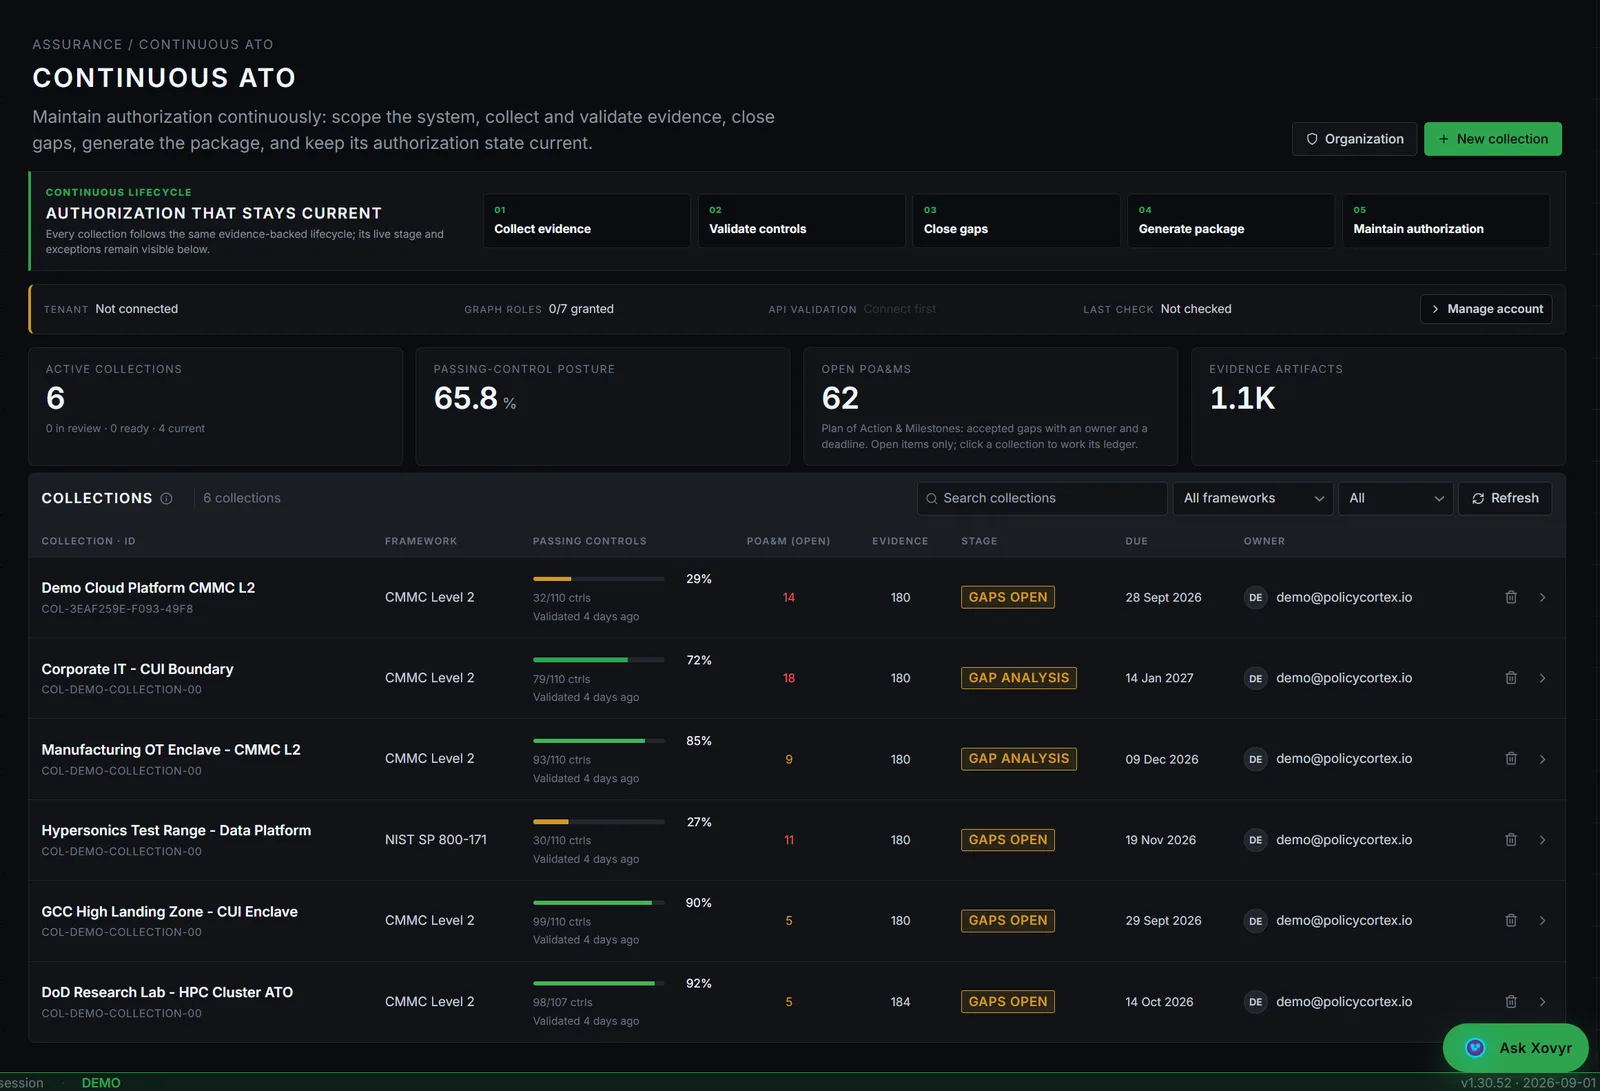
Three Questions Every Reviewer Asks—Answered from Your Record.
Every serious compliance review comes down to three questions. PolicyCortex answers each one from a sealed in-tenant record rather than manual screenshots or point-in-time questionnaires.
Missing observation is recorded as a fact, never hidden.
PolicyCortex records every missed observation window explicitly so your security team and your assessor see exact coverage boundaries.
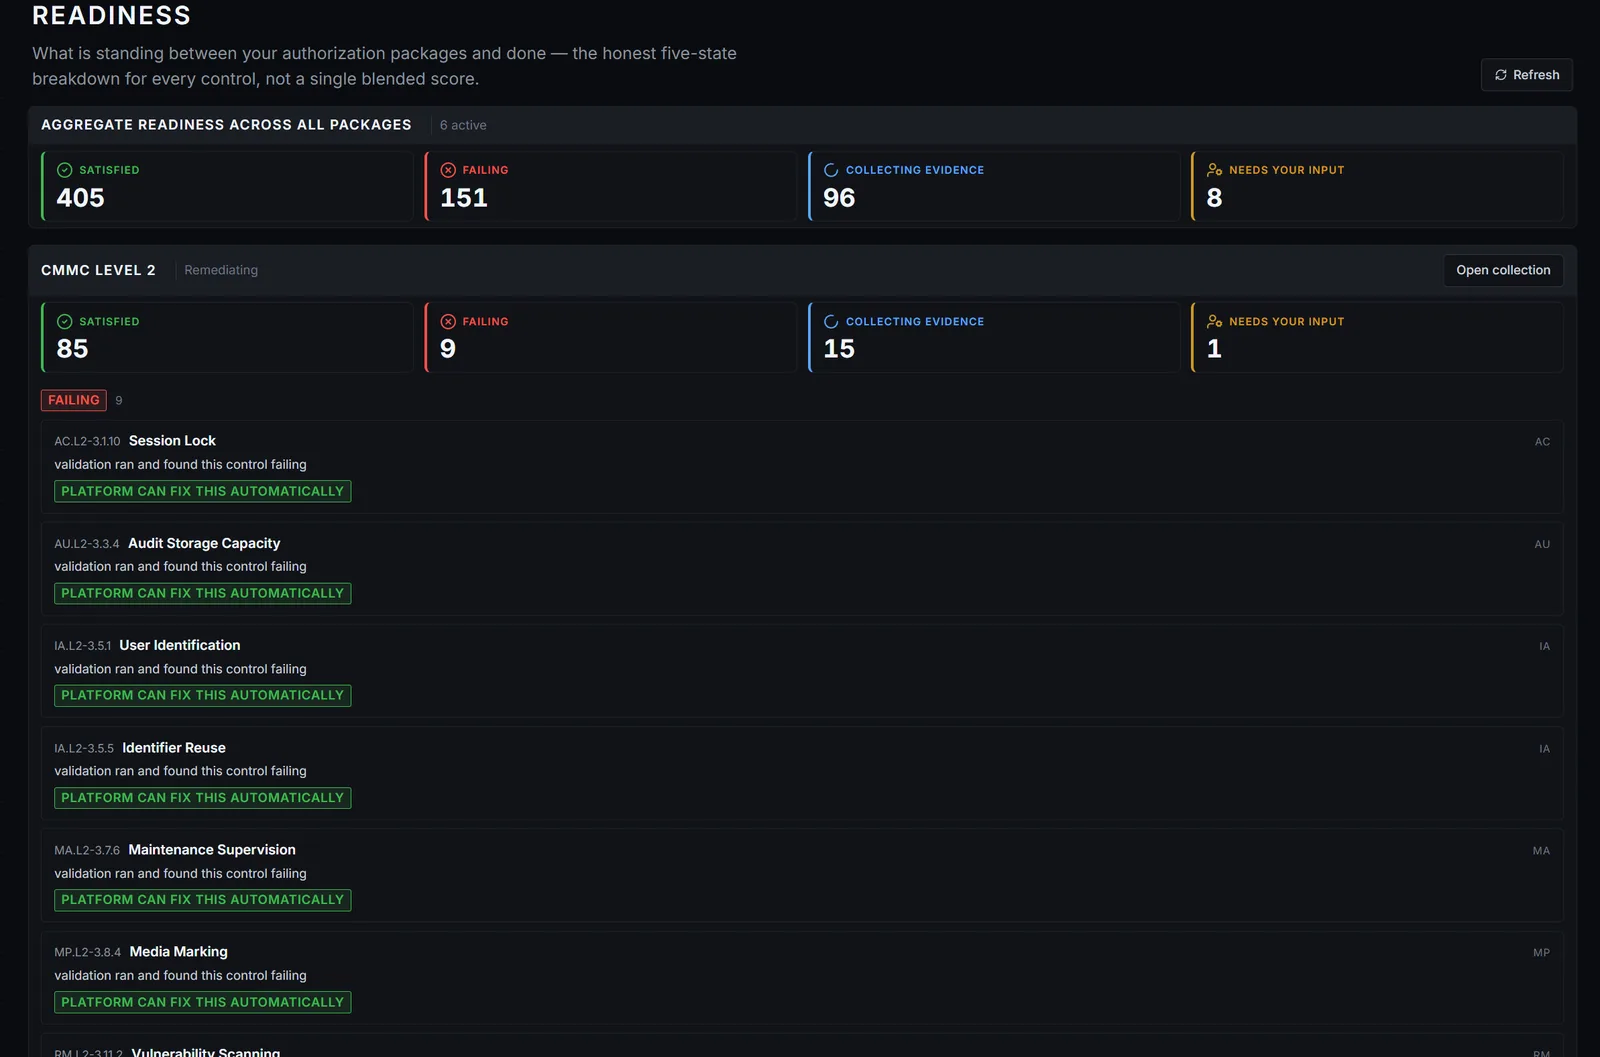
One Path from First Requirement to Assessor Review.
Start from zero or bring an existing compliance program. Each stage produces the verified record the next stage depends on.
Scope Your System & Boundary
Connect Azure Government, AWS GovCloud, Microsoft 365 GCC High, or GCP with read-only collectors inside your own cloud tenant. PolicyCortex maps your enclave assets, data flows, and applicable control catalog (CMMC Level 2, NIST SP 800-171, NIST SP 800-53, FedRAMP 20x, OMB M-25-21).
Observe & Seal Control State
Continuous read-only collectors evaluate control posture directly from live resource graphs and identity configurations. Every observation—and any missed collection window—is recorded in an append-only verification log.
Attribute Changes & Gate Remediation
Every configuration transition is paired with its approving authority, before/after state diff, and rollback snapshot. Automated remediation executes strictly inside operator-defined autonomy envelopes and blast-radius limits.
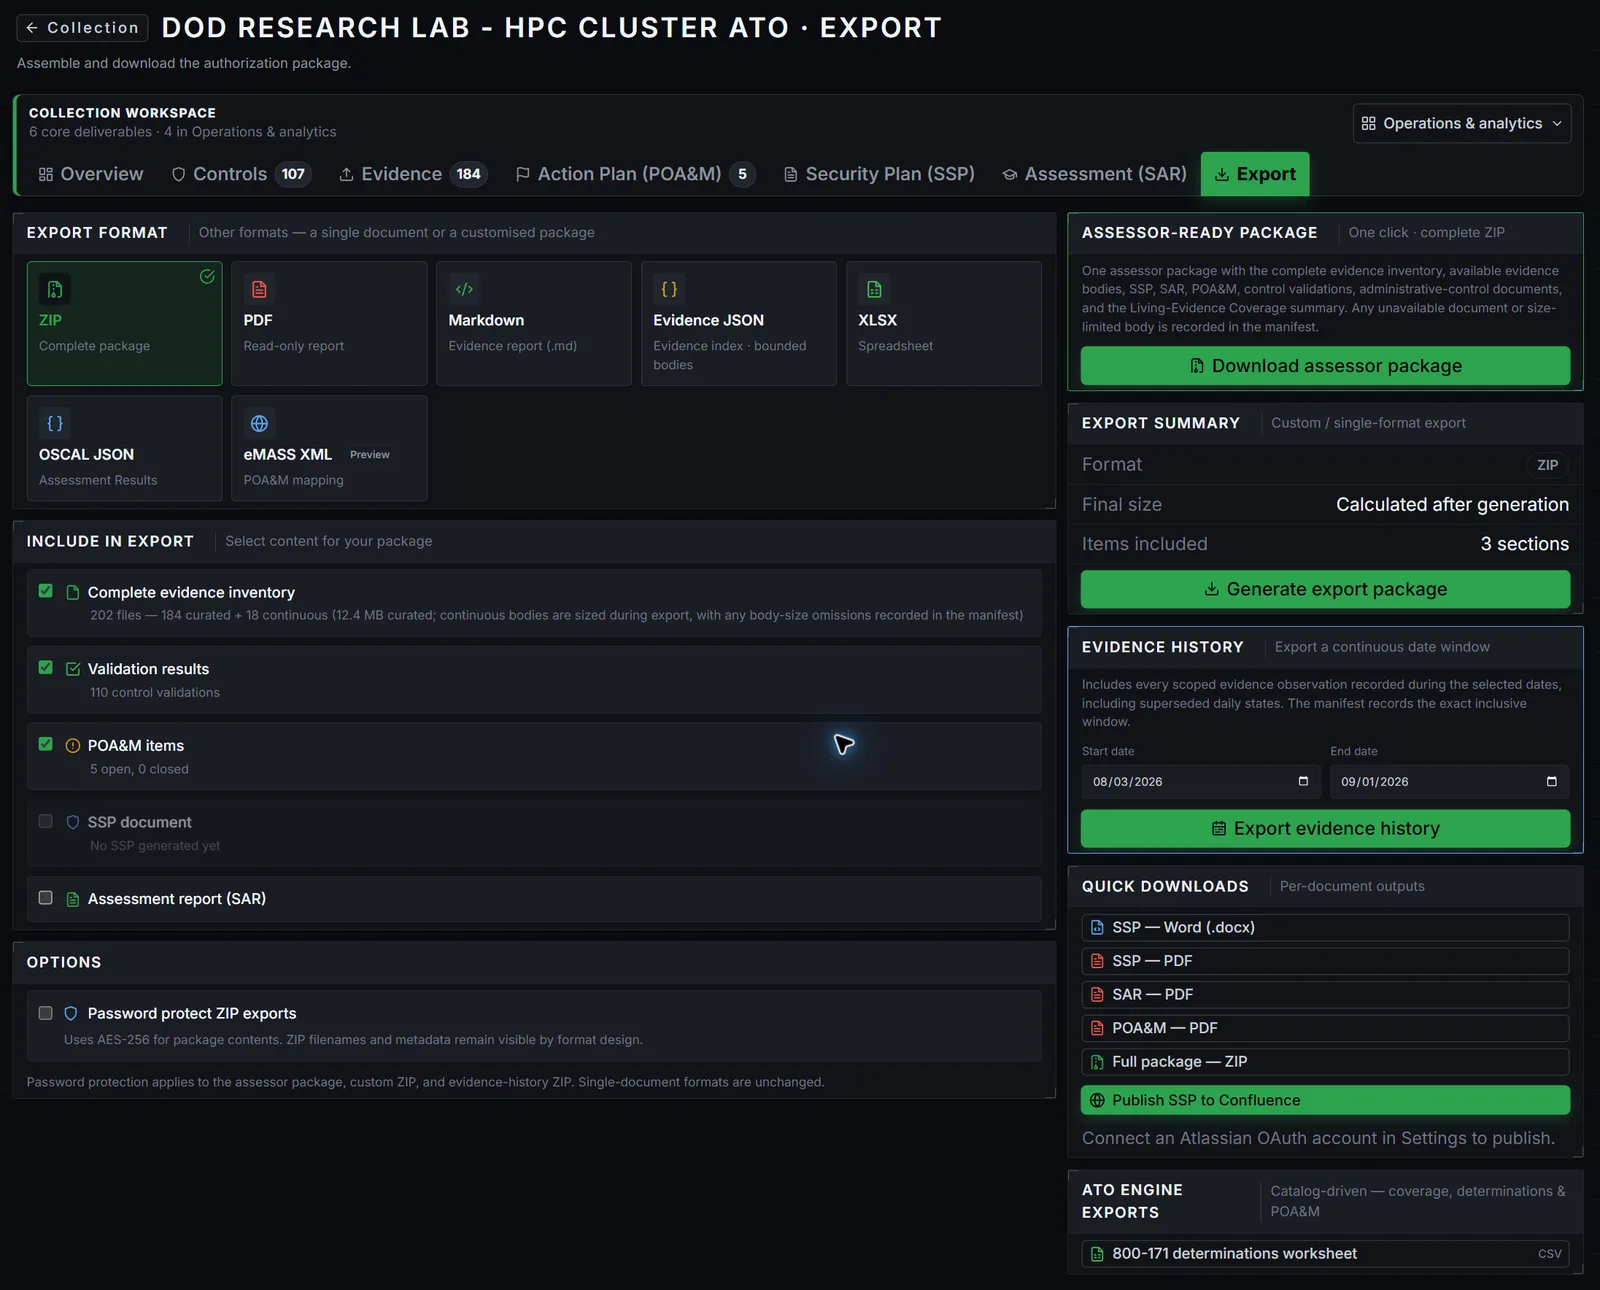
Compile Assessor-Ready Package
Generate your System Security Plan (SSP), Plan of Action & Milestones (POA&M), Security Assessment Report (SAR), OSCAL 1.1.2 JSON, and eMASS-compatible exports directly from the sealed evidence record.
Maintain Continuous Authorization
Instead of starting over before the next audit, keep every control determination, exception window, and change record current across multi-year operations.
The Review Package Comes Directly from the Work.
Stop pausing engineering for three months to assemble audit binders by hand. PolicyCortex compiles your complete authorization package directly from the in-tenant evidence record.
- Every control determination links to its raw observation and change history
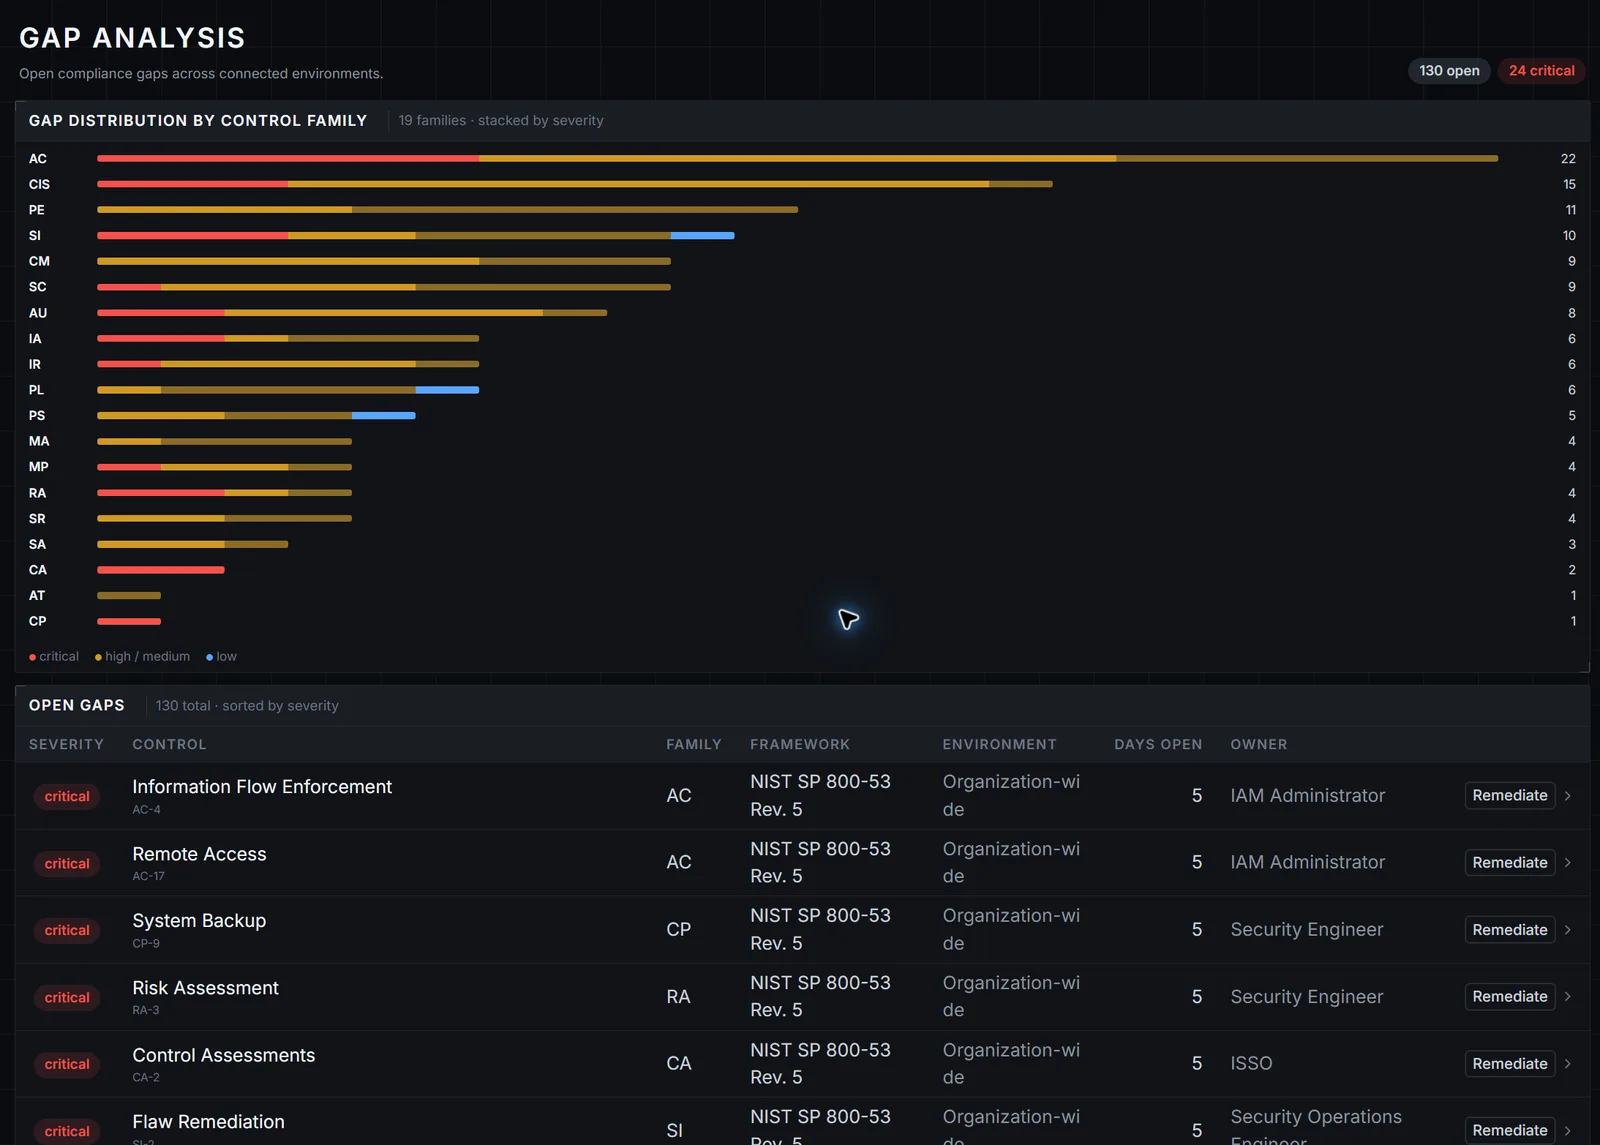
- Declared gaps and open POA&M items are surfaced honestly with owners and milestones
- Independent verifier CLI allows second-party assessors to verify package integrity offline
Live Control Implementation Narratives
Generated directly from observed system configuration, boundary topology, and control ownership—eliminating stale Word templates that contradict your actual environment.
Owned Findings & Remediation Milestones
Every open control gap and unexplained drift event is tracked with a named owner, severity, scheduled completion date, and linked remediation history.
Recomputable Evidence & Determinations
Binds each control determination to the exact timestamped observation and verification record so an independent reviewer reaches the same conclusion.
Machine-Readable Federal Deliverables
Exports validated NIST OSCAL 1.1.2 JSON, eMASS-compatible workbooks, and SPRS scoring worksheets for defense and federal authorization boundaries.
Asynchronous Control-Plane Verification Simulator.
Test how PolicyCortex evaluates asynchronous state snapshots, change transitions, and delegated authority across distributed cloud control planes.
Causal Control-Plane Verification
STATE(t_0..t_1) + MUTATION_READBACK(t_2) + DELEGATION_ENVELOPE(t_0..t_3) => INVARIANT_HELDPre-transition resource state, deterministic execution readback, and scoped principal delegation all bind to a single causal history across distributed control planes.
Cryptographic configuration state attested prior to transition execution.
Deterministic state transition verified with pre-staged rollback contract.
Delegation lease spans full pre-state and execution interval without revocation.
Start with a 14-Day Read-Only Evaluation.
Deploy PolicyCortex in read-only observation mode inside your Azure Government, AWS GovCloud, GCC High, or commercial cloud boundary. Keep the baseline findings and control posture report either way.